CCM — AES CCM mode encryption
Cipher block chaining - message authentication code (CCM) mode is an authenticated encryption algorithm designed to provide both authentication and confidentiality during data transfer. CCM combines counter mode encryption and CBC-MAC authentication. The CCM terminology "Message authentication code (MAC)" is called the "Message integrity check (MIC)" in Bluetooth terminology and also in this document.
The CCM block generates an encrypted keystream that is applied to input data using the XOR operation and generates the 4 byte MIC field in one operation. The CCM and radio can be configured to work synchronously. The CCM will encrypt in time for transmission and decrypt after receiving bytes into memory from the radio. All operations can complete within the packet RX or TX time. CCM on this device is implemented according to Bluetooth requirements and the algorithm as defined in IETF RFC3610, and depends on the AES-128 block cipher. A description of the CCM algorithm can also be found in NIST Special Publication 800-38C. The Bluetooth specification describes the configuration of counter mode blocks and encryption blocks to implement compliant encryption for BLE.
The CCM block uses EasyDMA to load key, counter mode blocks (including the nonce required), and to read/write plain text and cipher text.
The AES CCM supports three operations: key-stream generation, packet encryption, and packet decryption. All these operations are done in compliance with the Bluetooth specification.1
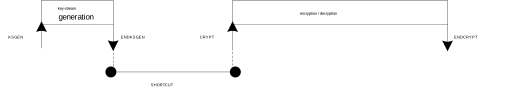
Key-steam generation
A new key-stream needs to be generated before a new packet encryption or packet decryption operation can be started.
A key-stream is generated by triggering the KSGEN task and an ENDKSGEN event will be generated when the key-stream has been generated.
Key-stream generation, packet encryption, and packet decryption operations utilize the configuration specified in the data structure pointed to by CNFPTR. It is necessary to configure this pointer and its underlying data structure, and the MODE register before the KSGEN task is triggered.
The key-stream will be stored in the AES CCM’s temporary memory area, specified by the SCRATCHPTR, where it will be used in subsequent encryption and decryption operations.
For default length packets (MODE.LENGTH = Default) the size of the generated key-stream is 27 bytes. When using extended length packets (MODE.LENGTH = Extended) the MAXPACKETSIZE register specifies the length of the key-stream to be generated. The length of the generated key-stream must be greater or equal to the length of the subsequent packet payload to be encrypted or decrypted. The maximum length of the key-stream in extended mode is 251 bytes, which means that the maximum packet payload size is 251.
If a shortcut is used between ENDKSGEN event and CRYPT task, the INPTR pointer and the OUTPTR pointers must also be configured before the KSGEN task is triggered.
Encryption
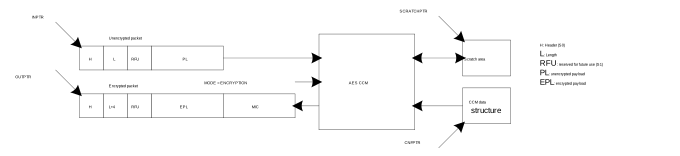
During packet encryption, the AES CCM will read the unencrypted packet located in RAM at the address specified in the INPTR pointer, encrypt the packet and append a four byte long Message Integrity Check (MIC) field to the packet.
Encryption is started by triggering the CRYPT task with the MODE register set to ENCRYPTION. An ENDCRYPT event will be generated when packet encryption is completed
The AES CCM will also modify the length field of the packet to adjust for the appended MIC field, that is, add four bytes to the length, and store the resulting packet back into RAM at the address specified in the OUTPTR pointer, see Encryption.
Empty packets (length field is set to 0) will not be encrypted but instead moved unmodified through the AES CCM.
The CCM supports different widths of the LENGTH field in the data structure for encrypted packets. This is configured in the MODE register.
Decryption
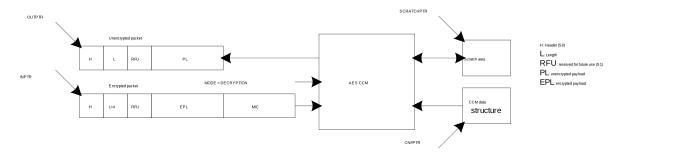
During packet decryption, the AES CCM will read the encrypted packet located in RAM at the address specified in the INPTR pointer, decrypt the packet, authenticate the packet’s MIC field and generate the appropriate MIC status.
Decryption is started by triggering the CRYPT task with the MODE register set to DECRYPTION. An ENDCRYPT event will be generated when packet decryption is completed
The AES CCM will also modify the length field of the packet to adjust for the MIC field, that is, subtract four bytes from the length, and then store the decrypted packet into RAM at the address pointed to by the OUTPTR pointer, see Decryption.
The CCM is only able to decrypt packet payloads that are at least 5 bytes long, that is, 1 byte or more encrypted payload (EPL) and 4 bytes of MIC. The CCM will therefore generate a MIC error for packets where the length field is set to 1, 2, 3 or 4.
Empty packets (length field is set to 0) will not be decrypted but instead moved unmodified through the AES CCM, these packets will always pass the MIC check.
The CCM supports different widths of the LENGTH field in the data structure for decrypted packets. This is configured in the MODE register.
AES CCM and RADIO concurrent operation
The CCM module is able to encrypt/decrypt data synchronously to data being transmitted or received on the radio.
In order for the CCM module to run synchronously with the radio, the data rate setting in the MODE register needs to match the radio data rate. The settings in this register apply whenever either the KSGEN or CRYPT tasks are triggered.
The data rate setting of the MODE register can also be overridden on-the-fly during an ongoing encrypt/decrypt operation by the contents of the RATEOVERRIDE register. The data rate setting in this register applies whenever the RATEOVERRIDE task is triggered. This feature can be useful in cases where the radio data rate is changed during an ongoing packet transaction.
Encrypting packets on-the-fly in radio transmit mode
When the AES CCM is encrypting a packet on-the-fly at the same time as the radio is transmitting it, the radio must read the encrypted packet from the same memory location as the AES CCM is writing to.
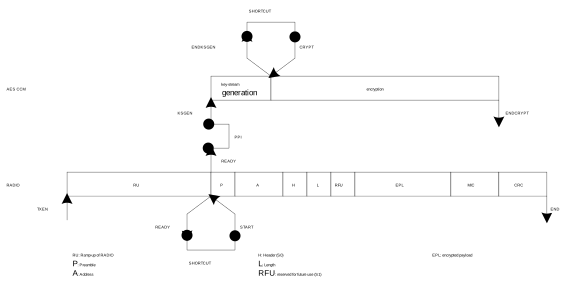
The OUTPTR pointer in the AES CCM must therefore point to the same memory location as the PACKETPTR pointer in the radio, see Configuration of on-the-fly encryption.
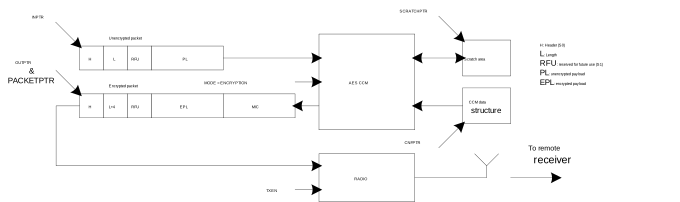
In order to match the RADIO’s timing, the KSGEN task must be triggered early enough to allow the key-stream generation to complete before the encryption of the packet shall start.
For short packets (MODE.LENGTH = Default) the KSGEN task must be triggered no later than when the START task in the RADIO is triggered. In addition the shortcut between the ENDKSGEN event and the CRYPT task must be enabled. This use-case is illustrated in On-the-fly encryption of short packets (MODE.LENGTH = Default) using a PPI connection using a PPI connection between the READY event in the RADIO and the KSGEN task in the AES CCM.
For long packets (MODE.LENGTH = Extended) the key-stream generation will need to be started even earlier, for example at the time when the TXEN task in the RADIO is triggered.
Decrypting packets on-the-fly in radio receive mode
When the AES CCM is decrypting a packet on-the-fly at the same time as the RADIO is receiving it, the AES CCM must read the encrypted packet from the same memory location as the RADIO is writing to.
The INPTR pointer in the AES CCM must therefore point to the same memory location as the PACKETPTR pointer in the RADIO, see Configuration of on-the-fly decryption.
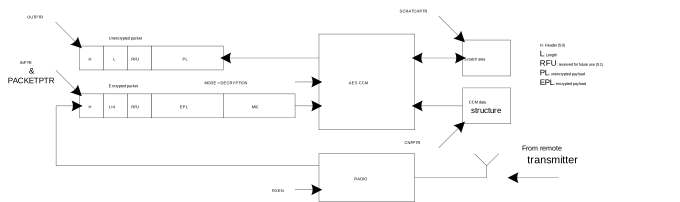
In order to match the RADIO’s timing, the KSGEN task must be triggered early enough to allow the key-stream generation to complete before the decryption of the packet shall start.
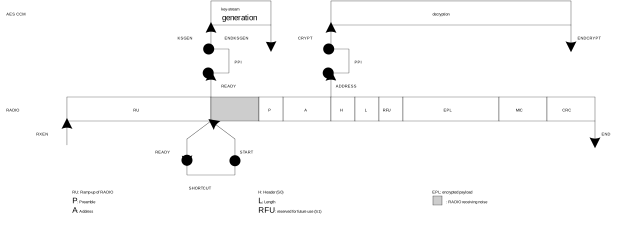
For short packets (MODE.LENGTH = Default) the KSGEN task must be triggered no later than when the START task in the RADIO is triggered. In addition, the CRYPT task must be triggered no earlier than when the ADDRESS event is generated by the RADIO.
If the CRYPT task is triggered exactly at the same time as the ADDRESS event is generated by the RADIO, the AES CCM will guarantee that the decryption is completed no later than when the END event in the RADIO is generated.
This use-case is illustrated in On-the-fly decryption of short packets (MODE.LENGTH = Default) using a PPI connection using a PPI connection between the ADDRESS event in the RADIO and the CRYPT task in the AES CCM. The KSGEN task is triggered from the READY event in the RADIO through a PPI connection.
For long packets (MODE.LENGTH = Extended) the key-stream generation will need to be started even earlier, for example at the time when the RXEN task in the RADIO is triggered.
CCM data structure
The CCM data structure is located in Data RAM at the memory location specified by the CNFPTR pointer register.
| Property | Address offset | Description |
|---|---|---|
| KEY | 0 | 16 byte AES key |
| PKTCTR | 16 | Octet0 (LSO) of packet counter |
| 17 | Octet1 of packet counter | |
| 18 | Octet2 of packet counter | |
| 19 | Octet3 of packet counter | |
| 20 | Bit 6 – Bit 0: Octet4 (7 most significant bits of packet counter, with Bit 6 being the most significant bit) Bit7: Ignored | |
| 21 | Ignored | |
| 22 | Ignored | |
| 23 | Ignored | |
| 24 | Bit 0: Direction bit Bit 7 – Bit 1: Zero padded | |
| IV | 25 | 8 byte initialization vector (IV) Octet0 (LSO) of IV, Octet1 of IV, … , Octet7 (MSO) of IV |
The NONCE vector (as specified by the Bluetooth Core Specification) will be generated by hardware based on the information specified in the CCM data structure from CCM data structure overview .
| Property | Address offset | Description |
|---|---|---|
| HEADER | 0 | Packet Header |
| LENGTH | 1 | Number of bytes in unencrypted payload |
| RFU | 2 | Reserved Future Use |
| PAYLOAD | 3 | Unencrypted payload |
| Property | Address offset | Description |
|---|---|---|
| HEADER | 0 | Packet Header |
| LENGTH | 1 | Number of bytes in encrypted payload including length of MIC Important: LENGTH will be 0 for empty packets since the MIC is not added to
empty packets |
| RFU | 2 | Reserved Future Use |
| PAYLOAD | 3 | Encrypted payload |
| MIC | 3 + payload length | ENCRYPT: 4 bytes encrypted MIC Important: MIC is not
added to empty packets |
EasyDMA and ERROR event
The CCM implements an EasyDMA mechanism for reading and writing to the RAM.
In cases where the CPU and other EasyDMA enabled peripherals are accessing the same RAM block at the same time, a high level of bus collisions may cause too slow operation for correct on the fly encryption. In this case the ERROR event will be generated.
The EasyDMA will have finished accessing the RAM when the ENDKSGEN and ENDCRYPT events are generated.
If the CNFPTR, SCRATCHPTR, INPTR and the OUTPTR are not pointing to the Data RAM region, an EasyDMA transfer may result in a HardFault or RAM corruption. See Memory for more information about the different memory regions.
Registers
| Base address | Peripheral | Instance | Description | Configuration | |
|---|---|---|---|---|---|
| 0x4000F000 | CCM | CCM | AES CCM mode encryption | ||
| Register | Offset | Description | |
|---|---|---|---|
| TASKS_KSGEN | 0x000 | Start generation of key-stream. This operation will stop by itself when completed. | |
| TASKS_CRYPT | 0x004 | Start encryption/decryption. This operation will stop by itself when completed. | |
| TASKS_STOP | 0x008 | Stop encryption/decryption | |
| TASKS_RATEOVERRIDE | 0x00C | Override DATARATE setting in MODE register with the contents of the RATEOVERRIDE register for any ongoing encryption/decryption | |
| EVENTS_ENDKSGEN | 0x100 | Key-stream generation complete | |
| EVENTS_ENDCRYPT | 0x104 | Encrypt/decrypt complete | |
| EVENTS_ERROR | 0x108 | CCM error event | Deprecated |
| SHORTS | 0x200 | Shortcuts between local events and tasks | |
| INTENSET | 0x304 | Enable interrupt | |
| INTENCLR | 0x308 | Disable interrupt | |
| MICSTATUS | 0x400 | MIC check result | |
| ENABLE | 0x500 | Enable | |
| MODE | 0x504 | Operation mode | |
| CNFPTR | 0x508 | Pointer to data structure holding AES key and NONCE vector | |
| INPTR | 0x50C | Input pointer | |
| OUTPTR | 0x510 | Output pointer | |
| SCRATCHPTR | 0x514 | Pointer to data area used for temporary storage | |
| MAXPACKETSIZE | 0x518 | Length of key-stream generated when MODE.LENGTH = Extended. | |
| RATEOVERRIDE | 0x51C | Data rate override setting. | |
TASKS_KSGEN
Address offset: 0x000
Start generation of key-stream. This operation will stop by itself when completed.
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | W | TASKS_KSGEN | Start generation of key-stream. This operation will stop by itself when completed. | ||||||||||||||||||||||||||||||||
Trigger | 1 | Trigger task | |||||||||||||||||||||||||||||||||
TASKS_CRYPT
Address offset: 0x004
Start encryption/decryption. This operation will stop by itself when completed.
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | W | TASKS_CRYPT | Start encryption/decryption. This operation will stop by itself when completed. | ||||||||||||||||||||||||||||||||
Trigger | 1 | Trigger task | |||||||||||||||||||||||||||||||||
TASKS_STOP
Address offset: 0x008
Stop encryption/decryption
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | W | TASKS_STOP | Stop encryption/decryption | ||||||||||||||||||||||||||||||||
Trigger | 1 | Trigger task | |||||||||||||||||||||||||||||||||
TASKS_RATEOVERRIDE
Address offset: 0x00C
Override DATARATE setting in MODE register with the contents of the RATEOVERRIDE register for any ongoing encryption/decryption
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | W | TASKS_RATEOVERRIDE | Override DATARATE setting in MODE register with the contents of the RATEOVERRIDE register for any ongoing encryption/decryption | ||||||||||||||||||||||||||||||||
Trigger | 1 | Trigger task | |||||||||||||||||||||||||||||||||
EVENTS_ENDKSGEN
Address offset: 0x100
Key-stream generation complete
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | EVENTS_ENDKSGEN | Key-stream generation complete | ||||||||||||||||||||||||||||||||
NotGenerated | 0 | Event not generated | |||||||||||||||||||||||||||||||||
Generated | 1 | Event generated | |||||||||||||||||||||||||||||||||
EVENTS_ENDCRYPT
Address offset: 0x104
Encrypt/decrypt complete
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | EVENTS_ENDCRYPT | Encrypt/decrypt complete | ||||||||||||||||||||||||||||||||
NotGenerated | 0 | Event not generated | |||||||||||||||||||||||||||||||||
Generated | 1 | Event generated | |||||||||||||||||||||||||||||||||
EVENTS_ERROR ( Deprecated )
Address offset: 0x108
CCM error event
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | EVENTS_ERROR | CCM error event | Deprecated | |||||||||||||||||||||||||||||||
NotGenerated | 0 | Event not generated | |||||||||||||||||||||||||||||||||
Generated | 1 | Event generated | |||||||||||||||||||||||||||||||||
SHORTS
Address offset: 0x200
Shortcuts between local events and tasks
INTENSET
Address offset: 0x304
Enable interrupt
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | C | B | A | ||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | ENDKSGEN | Write '1' to enable interrupt for event ENDKSGEN | ||||||||||||||||||||||||||||||||
Set | 1 | Enable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
| B | RW | ENDCRYPT | Write '1' to enable interrupt for event ENDCRYPT | ||||||||||||||||||||||||||||||||
Set | 1 | Enable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
| C | RW | ERROR | Write '1' to enable interrupt for event ERROR | Deprecated | |||||||||||||||||||||||||||||||
Set | 1 | Enable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
INTENCLR
Address offset: 0x308
Disable interrupt
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | C | B | A | ||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | ENDKSGEN | Write '1' to disable interrupt for event ENDKSGEN | ||||||||||||||||||||||||||||||||
Clear | 1 | Disable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
| B | RW | ENDCRYPT | Write '1' to disable interrupt for event ENDCRYPT | ||||||||||||||||||||||||||||||||
Clear | 1 | Disable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
| C | RW | ERROR | Write '1' to disable interrupt for event ERROR | Deprecated | |||||||||||||||||||||||||||||||
Clear | 1 | Disable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
MICSTATUS
Address offset: 0x400
MIC check result
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | R | MICSTATUS | The result of the MIC check performed during the previous decryption operation | ||||||||||||||||||||||||||||||||
CheckFailed | 0 | MIC check failed | |||||||||||||||||||||||||||||||||
CheckPassed | 1 | MIC check passed | |||||||||||||||||||||||||||||||||
ENABLE
Address offset: 0x500
Enable
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | |||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | ENABLE | Enable or disable CCM | ||||||||||||||||||||||||||||||||
Disabled | 0 | Disable | |||||||||||||||||||||||||||||||||
Enabled | 2 | Enable | |||||||||||||||||||||||||||||||||
MODE
Address offset: 0x504
Operation mode
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | C | B | B | A | |||||||||||||||||||||||||||||||
| Reset 0x00000001 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | MODE | The mode of operation to be used. The settings in this register apply whenever either the KSGEN or CRYPT tasks are triggered. | ||||||||||||||||||||||||||||||||
Encryption | 0 | AES CCM packet encryption mode | |||||||||||||||||||||||||||||||||
Decryption | 1 | AES CCM packet decryption mode | |||||||||||||||||||||||||||||||||
| B | RW | DATARATE | Radio data rate that the CCM shall run synchronous with | ||||||||||||||||||||||||||||||||
1Mbit | 0 | 1 Mbps | |||||||||||||||||||||||||||||||||
2Mbit | 1 | 2 Mbps | |||||||||||||||||||||||||||||||||
125Kbps | 2 | 125 Kbps | |||||||||||||||||||||||||||||||||
500Kbps | 3 | 500 Kbps | |||||||||||||||||||||||||||||||||
| C | RW | LENGTH | Packet length configuration | ||||||||||||||||||||||||||||||||
Default | 0 | Default length. Effective length of LENGTH field in encrypted/decrypted packet is 5 bits. A key-stream for packet payloads up to 27 bytes will be generated. | |||||||||||||||||||||||||||||||||
Extended | 1 | Extended length. Effective length of LENGTH field in encrypted/decrypted packet is 8 bits. A key-stream for packet payloads up to MAXPACKETSIZE bytes will be generated. | |||||||||||||||||||||||||||||||||
CNFPTR
Address offset: 0x508
Pointer to data structure holding AES key and NONCE vector
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | |||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | CNFPTR | Pointer to the data structure holding the AES key and the CCM NONCE vector (see Table 1 CCM data structure overview) | ||||||||||||||||||||||||||||||||
INPTR
Address offset: 0x50C
Input pointer
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | |||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | INPTR | Input pointer | ||||||||||||||||||||||||||||||||
OUTPTR
Address offset: 0x510
Output pointer
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | |||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | OUTPTR | Output pointer | ||||||||||||||||||||||||||||||||
SCRATCHPTR
Address offset: 0x514
Pointer to data area used for temporary storage
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | |||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SCRATCHPTR | Pointer to a scratch data area used for temporary storage during key-stream generation, MIC generation and encryption/decryption. The scratch area is used for temporary storage of data during key-stream generation and encryption. When MODE.LENGTH = Default, a space of 43 bytes is required for this temporary storage. MODE.LENGTH = Extended (16 + MAXPACKETSIZE) bytes of storage is required. | ||||||||||||||||||||||||||||||||
MAXPACKETSIZE
Address offset: 0x518
Length of key-stream generated when MODE.LENGTH = Extended.
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | A | A | A | A | A | A | |||||||||||||||||||||||||||
| Reset 0x000000FB | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 1 | 1 | 1 | 1 | 0 | 1 | 1 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | MAXPACKETSIZE | [0x001B..0x00FB] | Length of key-stream generated when MODE.LENGTH = Extended. This value must be greater or equal to the subsequent packet payload to be encrypted/decrypted. | |||||||||||||||||||||||||||||||
RATEOVERRIDE
Address offset: 0x51C
Data rate override setting.
Override value to be used instead of the setting of MODE.DATARATE. This override value applies when the RATEOVERRIDE task is triggered.
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | |||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | Access | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | RATEOVERRIDE | Data rate override setting. | ||||||||||||||||||||||||||||||||
1Mbit | 0 | 1 Mbps | |||||||||||||||||||||||||||||||||
2Mbit | 1 | 2 Mbps | |||||||||||||||||||||||||||||||||
125Kbps | 2 | 125 Kbps | |||||||||||||||||||||||||||||||||
500Kbps | 3 | 500 Kbps | |||||||||||||||||||||||||||||||||
Electrical specification
Timing specification
| Symbol | Description | Min. | Typ. | Max. | Units | ||||
|---|---|---|---|---|---|---|---|---|---|
| tkgen | Time needed for key-stream generation (given priority access to destination RAM block). | .. | .. | .. | µs |