SPU — System protection unit
SPU configures the access privileges for a peripheral.
SPU allows configuring access controls individually for each peripheral, and for some peripheral features. For example, a DPPI channel can be configured with different access controls than the peripheral.
SPU controls access according to TrustZone security attributes. If a peripheral or feature is configured as secure, only TrustZone secure accesses are allowed. If a peripheral or feature is configured as non-secure, then accesses are allowed both from secure and non-secure masters.
For some peripherals, the peripheral's DMA has a separate security configuration. If the peripheral is configured as secure, the peripheral's DMA can be configured to perform either secure or non-secure accesses. If the peripheral is configured as non-secure, the peripheral's DMA will always perform non-secure accesses.
General concepts
The SPU provides the register interface to configure and enforce the access privileges per peripheral, and where applicable, individual features of the peripheral such as GPIO pins, DPPI channels, etc.
Any accesses to a peripheral or a peripheral feature are validated against the SPU configuration for the security attributes.
Security attributes of a peripheral normally applies to all registers of the peripheral. However, some peripherals have split security to individual features within the peripheral, such as individual pins or DPPI channels. For these split feature peripherals, access is granted on a per-bit or per-register level. Unless mentioned otherwise, the term peripheral is used in the remainder of this section to refer to both a peripheral and an individual peripheral feature.
- See Instantiation to find the SPU instance used by the peripheral.
- The APB bus number can be extracted from the peripheral address. See Address format to find the APB bus number for a peripheral.
- See Block diagram for an overview over APB buses, the peripherals on that bus, and their controlling SPU instance.
See Address format for information on extracting the Peripheral slave index from a peripheral address.
        #define SPU_CORTEX_ADDRESS_REGION    (0x50000000)

        uint32_t perip_addr = NRF_SAADC_S_BASE;


        uint32_t apb_bus_number = (perip_addr & 0x00FC0000);
        uint32_t apb_slave_index = (perip_addr & 0x0003F000) >> 12;

        // Get the address to the SPU instance
        NRF_SPU_Type *p_spu = (NRF_SPU_Type*)(SPU_CORTEX_ADDRESS_REGION |
        apb_bus_number);

        // Configure PERIPH[n].PERM.SECATTR to secure for SAADC
        p_spu->PERIPH[apb_slave_index].PERM =
        (p_spu->PERIPH[apb_slave_index].PERM &
        ~SPU_PERIPH_PERM_SECATTR_Msk) |
        (SPU_PERIPH_PERM_SECATTR_Secure <<
        SPU_PERIPH_PERM_SECATTR_Pos)
See Instantiation to find the value of SLAVE_BITS for each SPU instance.
SPU supports secure and non-secure accesses based on TrustZone. On each access to a peripheral address, the security state of the master initiating the transaction is verified against the SPU security attribute configuration of the peripheral. The following figure shows a simplified view of the SPU registers controlling several internal modules.
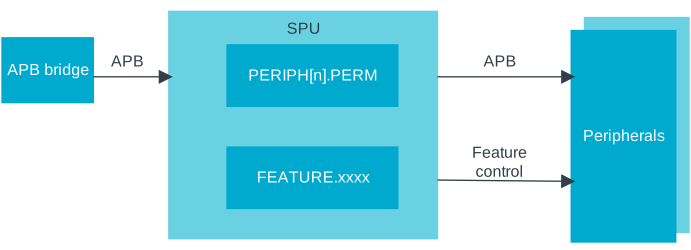
- A read operation that is not allowed by the SPU will always return a zero value on the bus, preventing information leak.
- A write operation that is not allowed by the SPU will be ignored.
An access error on peripherals managed by an SPU result in the PERIPHACCERR event on the SPU.
Peripheral access control
Peripheral access control depends on the security attributes.
Peripheral security attributes are defined in the Peripheral Instantiation table as one of the following:
- Always Secure (HF S)
- Access to the peripheral is always restricted to secure code.
- Always Non-secure (HF NS)
- Access to the peripheral is always allowed from both secure and non-secure code.
- User selectable (US)
- The security attribute can be configured for secure or non-secure access.
The full list of peripherals and their corresponding security attributes can be found in the Instantiation table in Memory section. For each peripheral with ID n, the register PERIPH[n].PERM.SECUREMAPPING will show whether the security attribute for this peripheral is user selectable or not.
The security attribute can be configured using the register PERIPH[n].PERM.SECATTR, if user selectable.
The DMA security attribute is determined as follows:
- If PERIPH[n].PERM.DMA is set to NoSeparateAttribute, then PERIPH[n].PERM.DMASEC cannot be configured, it has the same value as PERIPH[n].PERM.SECATTR.
- If PERIPH[n].PERM.DMA is set to SeparateAttribute and PERIPH[n].PERM.SECATTR is set to secure, then PERIPH[n].PERM.DMASEC is configurable. It is by default set to secure.
Secure code can access both secure peripherals and non-secure peripherals.
The DMA Privilege attribute is determined as follows:
- If PERIPH[n].PERM.DMA is set to NoSeparateAttribute, then PERIPH[n].PERM.DMAPRIVL cannot be configured, it has the same value as PERIPH[n].PERM.PRIVLATTR.
- If PERIPH[n].PERM.DMA is set to SeparateAttribute and PERIPH[n].PERM.PRIVLATTR is set to Privileged, then PERIPH[n].PERM.DMAPRIVL is configurable. It is by default set to Privileged.
Peripherals with split security
Peripherals with split security allow more detailed configuration.
When peripherals have split security, then the security of each feature in the peripheral can be configured individually using register FEATURE.
Each SPU instance can have different numbers of features. See the instantiation table for an overview of features supported by the split security peripherals.
Peripheral address mapping
Peripherals that have non-secure security mapping have their address starting with 0x4XXX_XXXX. Peripherals that have secure security mapping have their address starting with 0x5XXX_XXXX.
Peripherals with a user-selectable security mapping are available at an address starting with:
- 0x4XXX_XXXX, if the peripheral security attribute is set to non-secure
- 0x5XXX_XXXX, if the peripheral security attribute is set to secure
Secure code accessing the 0x5XXX_XXXX address range of a peripheral marked as non-secure will also result in a bus-error.
Peripherals with a split security mapping are available at an address starting with:
- 0x4XXX_XXXX for non-secure access and 0x5XXX_XXXX for secure access, if the peripheral
security attribute is set to non-secure
- Secure registers in the 0x4XXX_XXXX range are not visible for secure or non-secure code, and an attempt to access such a register will generate a peripheral access error, and result in write-ignore, read as zero behavior.
- Secure code can access both non-secure and secure registers in the 0x5XXX_XXXX range
- 0x5XXX_XXXX, if the peripheral security attribute is set to secure
Special considerations for peripherals with DMA master
Peripherals containing a DMA master can be configured so the security attribute of the DMA transfers is different from the security attribute of the peripheral itself. This allows a secure peripheral to do non-secure data transfers to or from the system memories.
- The DMA field of PERIPH[n].PERM.DMA is "SeparateAttribute"
- The peripheral itself is secure (PERIPH[n].PERM.SECATTR == 1)
Then it is possible to select the security attribute of the DMA transfers using the field DMASEC (PERIPH[n].PERM.DMASEC == Secure and PERIPH[n].PERM.DMASEC == NonSecure) in PERIPH[n].PERM.
Peripheral access error reporting
The SPU generates a peripheral access error event once access violation is detected.
- The faulty transfer will be blocked
- In case of a read transfer, the data will read as zero
- If supported by the master, feedback is sent to the master through specific bus error signals. If the master is a processor supporting Arm® TrustZone® for Cortex®-M, a SecureFault exception will be generated for security related errors.
- The PERIPHACCERR event will be triggered.
Feature access control
Access to the features can be restricted. A feature can be declared as secure so that only secure peripherals can access it.
The security attribute of a feature is configured by using corresponding SPU's feature register. When the secure attribute is set for a feature, only secure peripherals and code will be able to access that feature. For example, register FEATURE.GRTC.CC[n] is used to configure security for the capture-and-compare functionality of the GRTC peripheral. When the secure attribute is set, only secure code can access and use the corresponding capture-and-compare registers, tasks, and events.
See the SPU configuration to find the features supported by each SPU instance.
Registers
Instances
| Instance | Domain | Base address | TrustZone | Split access | Description | ||
|---|---|---|---|---|---|---|---|
| Map | Att | DMA | |||||
| SPU00 | GLOBAL | 0x50040000 | HF | S | NA | No | System protection unit SPU00 |
| SPU10 | GLOBAL | 0x50080000 | HF | S | NA | No | System protection unit SPU10 |
| SPU20 | GLOBAL | 0x500C0000 | HF | S | NA | No | System protection unit SPU20 |
| SPU30 | GLOBAL | 0x50100000 | HF | S | NA | No | System protection unit SPU30 |
Configuration
| Instance | Domain | Configuration |
|---|---|---|
| SPU00 | GLOBAL | Supports FEATURE.DPPIC[n] SLAVE_BITS=4 (number of address bits required to represent the peripheral slave index) |
| SPU10 | GLOBAL | Supports FEATURE.DPPIC[n] SLAVE_BITS=4 (number of address bits required to represent the peripheral slave index) |
| SPU20 | GLOBAL | Supports FEATURE.DPPIC[n] Supports FEATURE.GPIOTE[n] Supports FEATURE.GRTC[n] Supports FEATURE.GPIO[n] SLAVE_BITS=4 (number of address bits required to represent the peripheral slave index) |
| SPU30 | GLOBAL | Supports FEATURE.DPPIC[n] Supports FEATURE.GPIOTE[n] Supports FEATURE.GPIO[n] SLAVE_BITS=4 (number of address bits required to represent the peripheral slave index) |
Register overview
| Register | Offset | TZ | Description |
|---|---|---|---|
| EVENTS_PERIPHACCERR | 0x100 | A security violation has been detected on one or several peripherals | |
| INTEN | 0x300 | Enable or disable interrupt | |
| INTENSET | 0x304 | Enable interrupt | |
| INTENCLR | 0x308 | Disable interrupt | |
| INTPEND | 0x30C | Pending interrupts | |
| PERIPHACCERR.ADDRESS | 0x404 | Address of the transaction that caused first error. | |
| PERIPH[n].PERM | 0x500 | Get and set the applicable access permissions for the peripheral slave index n | |
| FEATURE.DPPIC.CH[n] | 0x680 | Security configuration for channel n of DPPIC | |
| FEATURE.DPPIC.CHG[n] | 0x6E0 | Security configuration for channel group n of DPPIC | |
| FEATURE.GPIOTE[n].CH[o] | 0x700 | Security configuration for channel o of GPIOTE[n] | |
| FEATURE.GPIOTE[n].INTERRUPT[o] | 0x720 | Security configuration for interrupt o of GPIOTE[n] | |
| FEATURE.GPIO[n].PIN[o] | 0x800 | Security configuration for GPIO[n] PIN[o] | |
| FEATURE.GRTC.CC[n] | 0xD00 | Security configuration for CC n of GRTC | |
| FEATURE.GRTC.PWMCONFIG | 0xD74 | Security Configuration for PWMCONFIG of GRTC | |
| FEATURE.GRTC.CLK | 0xD78 | Security configuration for CLKOUT/CLKCFG of GRTC | |
| FEATURE.GRTC.SYSCOUNTER | 0xD7C | Security configuration for SYSCOUNTERL/SYSCOUNTERH of GRTC | |
| FEATURE.GRTC.INTERRUPT[n] | 0xD80 | Security configuration for interrupt n of GRTC |
EVENTS_PERIPHACCERR
Address offset: 0x100
A security violation has been detected on one or several peripherals
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | EVENTS_PERIPHACCERR | A security violation has been detected on one or several peripherals | ||||||||||||||||||||||||||||||||
NotGenerated | 0 | Event not generated | |||||||||||||||||||||||||||||||||
Generated | 1 | Event generated | |||||||||||||||||||||||||||||||||
INTEN
Address offset: 0x300
Enable or disable interrupt
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | PERIPHACCERR | Enable or disable interrupt for event PERIPHACCERR | ||||||||||||||||||||||||||||||||
Disabled | 0 | Disable | |||||||||||||||||||||||||||||||||
Enabled | 1 | Enable | |||||||||||||||||||||||||||||||||
INTENSET
Address offset: 0x304
Enable interrupt
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | PERIPHACCERR | Write '1' to enable interrupt for event PERIPHACCERR | ||||||||||||||||||||||||||||||||
Set | 1 | Enable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
INTENCLR
Address offset: 0x308
Disable interrupt
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | PERIPHACCERR | Write '1' to disable interrupt for event PERIPHACCERR | ||||||||||||||||||||||||||||||||
Clear | 1 | Disable | |||||||||||||||||||||||||||||||||
Disabled | 0 | Read: Disabled | |||||||||||||||||||||||||||||||||
Enabled | 1 | Read: Enabled | |||||||||||||||||||||||||||||||||
INTPEND
Address offset: 0x30C
Pending interrupts
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | ||||||||||||||||||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | R | PERIPHACCERR | Read pending status of interrupt for event PERIPHACCERR | ||||||||||||||||||||||||||||||||
NotPending | 0 | Read: Not pending | |||||||||||||||||||||||||||||||||
Pending | 1 | Read: Pending | |||||||||||||||||||||||||||||||||
PERIPHACCERR.ADDRESS
Address offset: 0x404
Address of the transaction that caused first error.
The event PERIPHACCERR must be cleared to clear this register.
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | A | |||||||||||||||||||
| Reset 0x00000000 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | R | ADDRESS | Address | ||||||||||||||||||||||||||||||||
PERIPH[n].PERM
Address offset: 0x500 + (n × 0x4)
Get and set the applicable access permissions for the peripheral slave index n
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | F | E | D | C | B | B | A | A | |||||||||||||||||||||||||||
| Reset 0x8000002A | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 1 | 0 | 1 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | R | SECUREMAPPING | Read capabilities for TrustZone Cortex-M secure attribute | ||||||||||||||||||||||||||||||||
NonSecure | 0 | This peripheral is always accessible as a non-secure peripheral | |||||||||||||||||||||||||||||||||
Secure | 1 | This peripheral is always accessible as a secure peripheral | |||||||||||||||||||||||||||||||||
UserSelectable | 2 | Non-secure or secure attribute for this peripheral is defined by the PERIPH[n].PERM register | |||||||||||||||||||||||||||||||||
Split | 3 | This peripheral implements the split security mechanism. | |||||||||||||||||||||||||||||||||
| B | R | DMA | Read the peripheral DMA capabilities | ||||||||||||||||||||||||||||||||
NoDMA | 0 | Peripheral has no DMA capability | |||||||||||||||||||||||||||||||||
NoSeparateAttribute | 1 | Peripheral has DMA and DMA transfers always have the same security attribute as assigned to the peripheral | |||||||||||||||||||||||||||||||||
SeparateAttribute | 2 | Peripheral has DMA and DMA transfers can have a different security attribute than the one assigned to the peripheral | |||||||||||||||||||||||||||||||||
| C | RW | SECATTR | Peripheral security mapping This bit has effect only if PERIPH[n].PERM.SECUREMAPPING is UserSelectable or Split | ||||||||||||||||||||||||||||||||
Secure | 1 | Peripheral is mapped in secure peripheral address space | |||||||||||||||||||||||||||||||||
NonSecure | 0 | If SECUREMAPPING == UserSelectable: Peripheral is mapped in non-secure peripheral address space. If SECUREMAPPING == Split: Peripheral is mapped in non-secure and secure peripheral address space. | |||||||||||||||||||||||||||||||||
| D | RW | DMASEC | Security attribution for the DMA transfer This bit has effect only if PERIPH[n].PERM.SECATTR is set to secure and PERIPH[n].PERM.DMA is set to SeparateAttribute. | ||||||||||||||||||||||||||||||||
Secure | 1 | DMA transfers initiated by this peripheral have the secure attribute set | |||||||||||||||||||||||||||||||||
NonSecure | 0 | DMA transfers initiated by this peripheral have the non-secure attribute set | |||||||||||||||||||||||||||||||||
| E | RW | LOCK | Register lock | ||||||||||||||||||||||||||||||||
Unlocked | 0 | This register can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | The content of this register can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
| F | R | PRESENT | Indicates if a peripheral is present with peripheral slave index n | ||||||||||||||||||||||||||||||||
NotPresent | 0 | Peripheral is not present | |||||||||||||||||||||||||||||||||
IsPresent | 1 | Peripheral is present | |||||||||||||||||||||||||||||||||
FEATURE.DPPIC.CH[n]
Address offset: 0x680 + (n × 0x4)
Security configuration for channel n of DPPIC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.DPPIC.CHG[n]
Address offset: 0x6E0 + (n × 0x4)
Security configuration for channel group n of DPPIC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GPIOTE[n].CH[o]
Address offset: 0x700 + (n × 0x40) + (o × 0x4)
Security configuration for channel o of GPIOTE[n]
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GPIOTE[n].INTERRUPT[o]
Address offset: 0x720 + (n × 0x40) + (o × 0x4)
Security configuration for interrupt o of GPIOTE[n]
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GPIO[n].PIN[o]
Address offset: 0x800 + (n × 0x80) + (o × 0x4)
Security configuration for GPIO[n] PIN[o]
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GRTC.CC[n]
Address offset: 0xD00 + (n × 0x4)
Security configuration for CC n of GRTC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GRTC.PWMCONFIG
Address offset: 0xD74
Security Configuration for PWMCONFIG of GRTC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GRTC.CLK
Address offset: 0xD78
Security configuration for CLKOUT/CLKCFG of GRTC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GRTC.SYSCOUNTER
Address offset: 0xD7C
Security configuration for SYSCOUNTERL/SYSCOUNTERH of GRTC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||
FEATURE.GRTC.INTERRUPT[n]
Address offset: 0xD80 + (n × 0x4)
Security configuration for interrupt n of GRTC
| Bit number | 31 | 30 | 29 | 28 | 27 | 26 | 25 | 24 | 23 | 22 | 21 | 20 | 19 | 18 | 17 | 16 | 15 | 14 | 13 | 12 | 11 | 10 | 9 | 8 | 7 | 6 | 5 | 4 | 3 | 2 | 1 | 0 | |||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ID | B | A | |||||||||||||||||||||||||||||||||
| Reset 0x00100010 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 0 | 1 | 0 | 0 | 0 | 0 | |||
| ID | R/W | Field | Value ID | Value | Description | ||||||||||||||||||||||||||||||
| A | RW | SECATTR | SECATTR feature | ||||||||||||||||||||||||||||||||
NonSecure | 0 | Feature is available for non-secure usage | |||||||||||||||||||||||||||||||||
Secure | 1 | Feature is reserved for secure usage | |||||||||||||||||||||||||||||||||
| B | RW | LOCK | LOCK feature | ||||||||||||||||||||||||||||||||
Unlocked | 0 | Feature permissions can be updated | |||||||||||||||||||||||||||||||||
Locked | 1 | Feature permissions can not be changed until the next reset When Locked, it remains Locked until the next reset cycle. | |||||||||||||||||||||||||||||||||